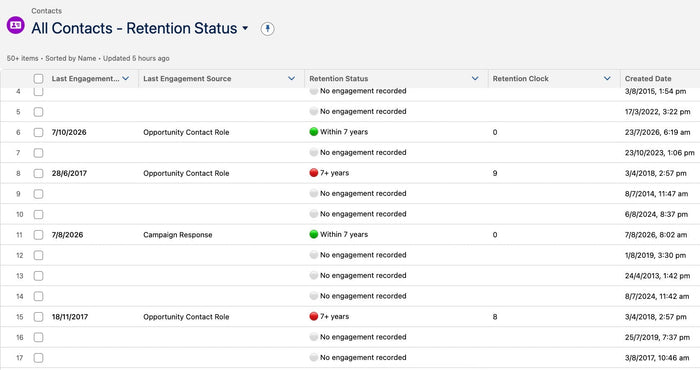
Old donor data is a risk your Board can measure and reduce
Equitable Philanthropy and EP Law have released a free Donor Data Retention Policy template for Australian charities. Blaze Your Trail’s Retention Clock helps Boards...
This week, one of our customers was setting up an organisation-wide email address in Salesforce so their CEO's emails could be sent from Salesforce under her name.

Salesforce sent the verification email, the CEO clicked the link, and it didn't work. They tried again. Same result.
It turns out this is how Salesforce now works, and it caught us by surprise too. Here's what's going on and how to fix it.
When you add a new organisation-wide email address in Salesforce, Salesforce sends a verification email to that address. You'd expect the owner of the inbox to click the link and be done.
But since the Summer '26 release, that often doesn't work. You may also notice the email greets the wrong person: it shows the name of the admin who added the address, not the person who owns the inbox.
In Summer '26, Salesforce introduced a security measure for email address verification. The verification link is now tied to the session of the admin who added the address. In plain English, the link only works when it's opened by that admin, in the browser where they're already logged in to Salesforce.
So when the inbox owner clicks the link themselves, or when a different admin tries it, Salesforce doesn't recognise the session and the verification fails.
Salesforce Support has confirmed this is working as designed. It's there to keep verification secure, and no fix is planned.
The release came out three months ago, and this was the first time we'd come across it, so if it's tripped you up too, you're not alone.
The person who owns the inbox doesn't need to log in to Salesforce at all. They just pass the email on.
Equitable Philanthropy and EP Law have released a free Donor Data Retention Policy template for Australian charities. Blaze Your Trail’s Retention Clock helps Boards...
Two critical PHP security flaws, known as PHP2Shell, could affect any website built on WordPress. Here are four simple steps to check your server’s...
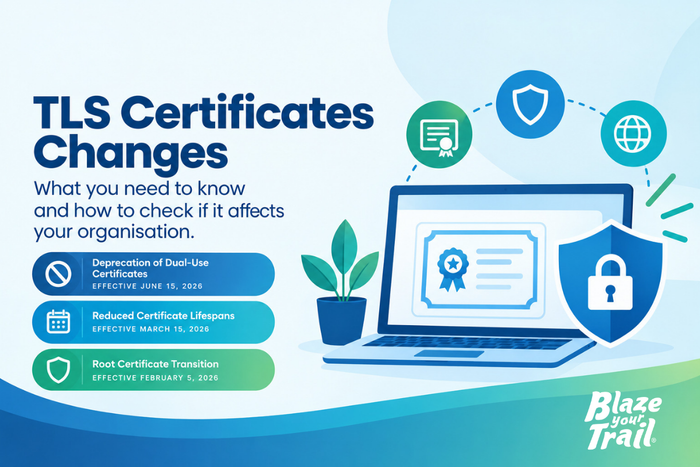
TLS Certificate changes: Deprecation of Dual-Use Certificates effective June 15, 2026, Reduced Certificate Lifespans effective March 15, 2026, and Root Certificate Transition effective February...