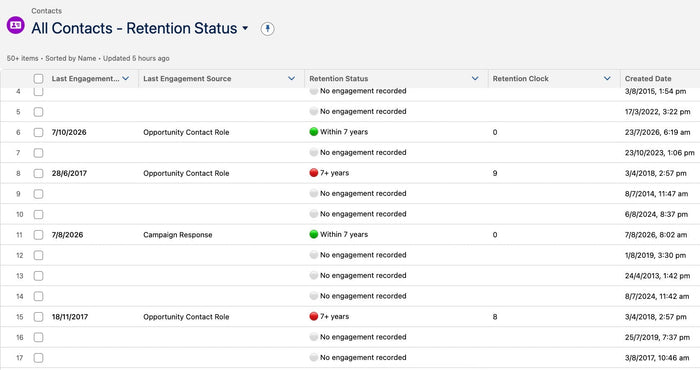
Old donor data is a risk your Board can measure and reduce
Equitable Philanthropy and EP Law have released a free Donor Data Retention Policy template for Australian charities. Blaze Your Trail’s Retention Clock helps Boards...
Recent hacking attacks show how easily fake apps can expose sensitive Salesforce data. A breach can damage your reputation, disrupt operations, and put your supporters at risk.
Over the past week, a wave of Salesforce-related hacking attacks has hit companies like Chanel, Qantas, Adidas, Victoria’s Secret, and even Google.
The main tactic? Hackers tricking staff into installing fake apps—most notably a counterfeit “Data Loader” tool—which gave them access to sensitive Salesforce data.
In response to the Google breach, Salesforce reminded customers to review their security best practices, including multi-factor authentication (MFA), least privilege access, and careful management of connected apps.
Think of it this way: Salesforce is like a landlord. They provide the building, locks, and security guidance—but if tenants leave their doors unlocked, there’s only so much Salesforce can do.
A Salesforce data breach could:
Be very selective about who gets System Administrator access. Only give this profile to people you absolutely trust, who have proven Salesforce knowledge and experience.
A non-disclosure agreement won’t help if an inexperienced admin is tricked into installing malicious software. One mistake could expose all of your Salesforce data.
It sounds easy, but sometimes we can’t find the time to do everything on our to-do list. Keeping your supporters’ trust starts with keeping their data safe. If you’d like guidance on securing Salesforce for your organisation, please contact us — we’re here to help!
Equitable Philanthropy and EP Law have released a free Donor Data Retention Policy template for Australian charities. Blaze Your Trail’s Retention Clock helps Boards...
Two critical PHP security flaws, known as PHP2Shell, could affect any website built on WordPress. Here are four simple steps to check your server’s...
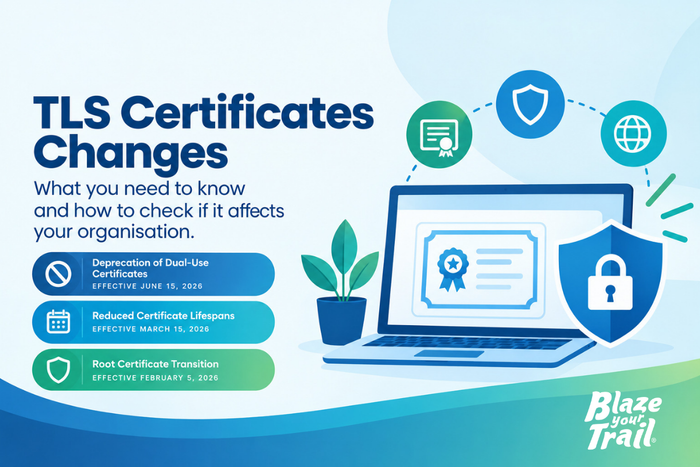
TLS Certificate changes: Deprecation of Dual-Use Certificates effective June 15, 2026, Reduced Certificate Lifespans effective March 15, 2026, and Root Certificate Transition effective February...