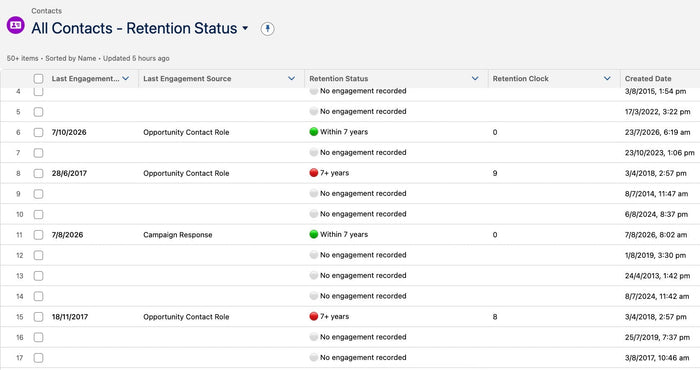
Old donor data is a risk your Board can measure and reduce
Equitable Philanthropy and EP Law have released a free Donor Data Retention Policy template for Australian charities. Blaze Your Trail’s Retention Clock helps Boards...
Many of us received the recent Salesforce email titled: “Immediate Action Required: Verify Your Domains for Email Security.” Salesforce is now enforcing strict domain ownership verification.

Starting March 9, 2026:
Emails sent from unverified domains will not be delivered.
If your organisation sends emails from Salesforce using your own domain (e.g. @yourorg.org). Action is required.
To remain compliant and avoid disruption, you must verify your domain using one of Salesforce’s approved methods. The recommended method is:
Setting up DKIM verifies your domain ownership and improves email deliverability. The full internal step-by-step guide is available here:
DKIM Keys, DMARC & SPF Policy for Salesforce – March 2026
This document includes:
How to create DKIM keys in Salesforce
How to publish CNAME records in DNS
How to activate your DKIM key
How Salesforce handles 30-day DKIM rotation
How to configure SPF and DMARC records
Mailchimp (Mandrill) authentication notes
Please follow this How-To Guide exactly to ensure proper configuration.
From Salesforce’s notification:
New sending domains → Immediate verification required
Existing sending domains
Sandboxes → Verify by March 30, 2026
Production orgs → Verify by April 27, 2026
After enforcement, unverified domains will not be allowed to send email.
To continue sending emails from Salesforce without disruption:
Ensure DKIM is set up and activated
Ensure required DNS records are published
Ensure SPF and DMARC are in place
Confirm DNS propagation before activation
All technical instructions are documented in the attached PDF.
This update strengthens email security and protects our sender reputation, but it does require timely configuration.
Please refer to the attached guide and complete domain verification as soon as possible.
If you need assistance, contact the team before the deadline.
Equitable Philanthropy and EP Law have released a free Donor Data Retention Policy template for Australian charities. Blaze Your Trail’s Retention Clock helps Boards...
Two critical PHP security flaws, known as PHP2Shell, could affect any website built on WordPress. Here are four simple steps to check your server’s...
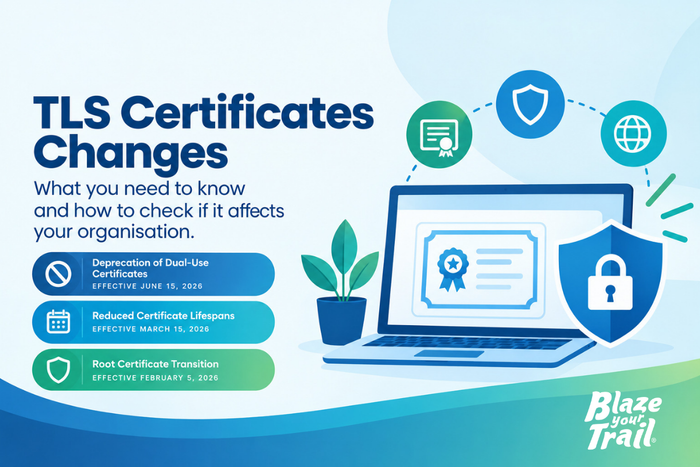
TLS Certificate changes: Deprecation of Dual-Use Certificates effective June 15, 2026, Reduced Certificate Lifespans effective March 15, 2026, and Root Certificate Transition effective February...